Posts tagged #internet
59 posts
-
2026-03-01
-
2026-03-01
-
2026-02-23
We Are Finally Off Discord
We are finally off discord and on a self-hosted system that should be better suited.
-
2024-04-12
Riders.ai | Introducing Learntech - Playtech
No course has ever been this engaging and effective in teaching hard-to-master STEM skills!
-
2023-01-15
GitHub - volution/z-tokens: z-tokens -- random tokens generation and related tools
This is a standalone password generator. I think that because it does’t know the email or account name that the password is used with, the risk that the app itself is malware is small… i think… Author says: “z-tokens -- random tokens generation and related tools - GitHub - volution/z-tokens: z-tokens -- random tokens generation and related tools”
-
2022-04-24
Custom Shirts - Design Custom T-Shirts Online | 40% OFF
Custom Shirts! #1 Leader in Custom T-Shirts. Create custom t-shirts for your team, business, school, event and more. FREE SHIPPING!
-
2022-02-01
-
2022-01-24
Custom vinyl stickers, decals, labels. High quality printing at low prices!
Get custom vinyl stickers, die cuts, window decals, and roll labels printed with your design. The original Sticker Guy, stickin since 1993
-
2021-08-13
-
2021-05-28
The Lab-Leak Hypothesis
The Lab-Leak Hypothesis For decades, scientists have been hot-wiring viruses in hopes of preventing a pandemic, not causing one. But what if …? May 29, 2021 at 12:54AM
-
2021-05-28
The Sudden Rise of the Lab-Leak Theory
The Sudden Rise of the Lab-Leak Theory Scientists and political commentators are no longer dismissing the possibility that COVID-19 emerged from a Chinese laboratory. What changed? May 29, 2021 at 01:00AM
-
2021-04-13
QUT Robot Academy
University-level, short video lessons and full online courses to help you understand and prepare for this technology of the future.
-
2021-04-06
-
2021-04-06
Seth Ladd's Blog: Ruby, Rails, OpenID, and Google Integration for the Busy Developer
Useful info about how to authenticate from Rails to Google
-
2021-04-06
Sheetsu Documentation
Get data from Google Spreadsheet in a matter of seconds. You can copy the HTML Snippet and paste it into your website without any code. If you are developer, you can use one of many languages or frameworks Sheetsu supports like Ruby, Node, React, JavaScript Python, PHP, JQuery, C#, Swift, or R.
-
2021-04-06
-
2021-04-06
an SSH Tarpit « null program
Kind of interesting about security, hacking, protocols and ssh
-
2021-04-06
How bad can it git? Characterizing secret leakage in public GitHub repositories
Everyone knows by now to never put secret keys in code, right?
-
2021-04-06
strong_password v0.0.7 rubygem hijacked
Interesting description of how a public library or gem can be taken over, and modified to create an all powerful backdoor.
-
2021-04-06
Best Selling Watches on Sale: Top Men's & Women's Watches Online
Looks like a great site for buying cheap watches!
-
2021-04-06
CODAP - Common Online Data Analysis Platform
Looks really useful.
-
2021-04-06
Rodauth: A Refreshing Authentication Solution for Ruby | Janko's Blog
Always nice to see alternatives to devise but this is just as complicated. I haven’t used it but my question is how much of the user facing UI does it provide and how do you customize it?
-
2013-12-07
[Pro-Tip] When writing a delicate email, enter the To: last
So, if you are writing one of those emails that you have to get right, and you plan to check and proof and think about, then don’t start by typing the To:. As long as you don’t type the To: you can’t accidentally send it out before you finish writing it. Once you write the To:, and accidental or careless send will possibly cause collateral damage if you’re not done word smithing your message.
-
2013-10-01
Interesting behind-the-scenes look at NSA
Zegart joins scholars at NSA for rare briefing on spy agency’s woes – CISAC:
CISAC Co-Director Amy Zegart and nine other national security and intelligence scholars were recently invited to the headquarters of the National Security Agency in Fort Meade, Md., for unprecedented talks with high-ranking officials. They discussed cybersecurity, the plummeting public trust in the agency, its relationship with Congress and how to rebuild the agency’s reputation and rethink its program operations.
-
2013-09-25
[security] Fascinating ID Theft saga
It is quite amazing (but not surprising) the degree of sophistication, care, and patience these hackers apply. Their engineering and business savvy are at the same level as the best of Google and Amazon.
Data Broker Giants Hacked by ID Theft Service — Krebs on Security:
An identity theft service that sells Social Security numbers, birth records, credit and background reports on millions of Americans has infiltrated computers at some of America’s largest consumer and business data aggregators, according to a seven-month investigation by KrebsOnSecurity.
-
2013-09-05
The other side of the Snowden story
What Did Edward Snowden Get Wrong? Everything | RAND:
Incidents like the Snowden affair put my former colleagues in the intelligence community in an impossible position. Yes, the official explanations about the virtues of data-collection efforts can sound self-justifying and vague. But they’re still right. I know firsthand that Gen. Keith Alexander, the NSA director, is telling the truth when he talks about plots that have been preempted and attacks that have been foiled because of intelligence his agency collected. I know because I was on the inside, I have long held security clearances, and I participated in many of the activities he describes.
-
2013-08-28
Double Agent?
Read more →I am reading a really cool book right now: GARBO: The Spy Who Saved D-Day
a about a double agent and an elaborate look behind the curtain of espionage during WW2. Makes me wonder about the amazing amoung of leaked detail about a missle strike on Syria.
Could it be a total spoof, and even as we speak, special forces are infiltrating Damascus and doing their thing? And “whoops” – did I just give it all away?
...
-
2013-08-27
Trouble in password land, again?
Read more →I was rather pleased with myself!
I have been changing all my passwords to easier to remember but supposedly harder to crack passwords. I had read, on good authority, that making a password longer was a better protection that using lots of funky characters. So for example, I set my gmail password to “when-i-need-to-send-mail”. Nice and long. Also, sites that check a password for safety, tell me that’s a good password. http://www.passwordmeter.com gives it a 100% – “Very Strong”.
I admit that my inutition was confused. I was using common english words. Even though I have a lot of them and a long overall password length, it did feel like it was not as secure as the experts were telling me…
...
-
2013-07-19
Love/Hate Gmail
Read more →I’ve been using Gmail like forever now and have converted many friends and family members to using it. It’s great and it’s ridiculously cheap. Coupled with a good ad-suppressor plug-in for Safari (Mac) it works well for me. I do access it, almost always, via the desktop Mail app on Mac OSX, so I don’t experience it’s UI all the time.
But the Gmail UI is quite bizarre, with multiple different ways to do similar things, weird drop down menus and weird functionality in places. So it’s a little annoying, but, it does scale, it is cheap, and it is up almost all the time.
I only briefly considered the idea of moving from Gmail to something else when reading this article, but within seconds knew ...
-
2013-07-08
[GEEKY] Social login buttons considered harmful
Read more →You probably don’t know what a social login button is so forgive this bit of geekyness. I am sure you’ve seen them: “login with facebook or twitter?” If an app or a site wants to “save you the trouble” of registering a username and password, they may “make your life easier” by allowing you to register using your facebook or twitter password. Conventional wisdom in the world of apps has been that this is a user requirement, and plus beneficial to the business as well. Here’s an interesting article that refutes that belief, at least in certain significant scenarios.
...
-
2013-04-12
Great tips for dealing with email
This is a tired topic but this article from the New York Times does have some good tips on managing your avalanche of email …
“…There’s no quick fix. But set aside a few hours one afternoon, brew a pot of coffee, get a tasty snack, put on your favorite playlist and roll up your sleeves. It’s time to tame your in-box…” (from “How to Lighten the Crush of Email“)
-
2012-11-07
Check out WriteThatName
I’ve been using a app called “WriteThatName” which very helpfully scans the emails I receive for signature blocks with people’s name. It takes that info and correctly parses it and adds it to my google contacts. Super nice. I recommend it!
-
2012-10-19
Beautiful Outlook
Read more →I don’t know why this has not gotten more press. You should take a look at Microsoft’s new Gmail killer, outlook.com. It’s a totally web based email client, like Gmail, but the user experience is miles and miles better than Gmail.
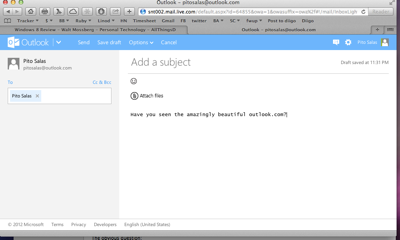
Now I am a huge Gmail user, and generally I get along really well with it. It has years of my emails and I have fully mastered its tricks and hacks. It works, it’s reliable and it’s free.
But boy, as a user interface, isn’t Gmail UGLY?
And now look at Microsoft’s ...
-
2012-10-18
Securing or attacking Industrial Control Systems
Read more →It turns out that Kaspersky Labs is developing a brand new operating system specifically designed to be used in embedded industrial systems and industrial control systems.
The obvious question:
“First I’ll answer the most obvious question: how will it b...
-
2012-07-26
Sparrow vs. Mail.app and Mountain Lion
Read more →Did you hear that Google bought Sparrow? Sparrow is a really cool email client that I for one have been using very happily for a while now.
Did you hear the announcement that there would be no more development of sparrow?
Did you hear that some people were upset at this, while others defended Sparrow’s “right” to let themselves be sold? (Huh????)
Anyway, I am not getting into that discussion. I was selfishly sad, because I am very fond of Sparrow and I know (from first hand knowledge, m...
-
2012-06-07
LinkedIn Passwords: Who stores passwords in the clear
Read more →I am a pretty regular LinkedIn user, so the news that some unspecified number of LinkedIn users had their passwords compromised was of some interest to me.
Here’s what a recent post on their blog says:
“We want to provide you with an update on this morningâs reports of stolen passwords. We can confirm that some of the passwords that were compromised correspond to LinkedIn accounts. We are continuing to investigate this situation and here is what we are pursuing as far as next steps for the compromised accounts….” (from ...
-
2012-04-04
Email Rookie Mistakes
Read more →I’ve watched some people struggling with some email blow ups and frustrations over the years and I was just thinking about some of the ways I’ve developed to avoid them. I am not going into the best salutation or the best conclusion but more touchy-feely things. Here are my guidelines:
Write the email as if it might show up on the front page of the paper tomorrow morning. Because it might. Or it might be forwarded to the wrong person. Or you may accidentally send it to the wrong person. Worse, to a long mailing list of the wrong people. Don’t include anything that you would be embarrassed or worse, ashamed, to have to explain. ...
-
2012-02-13
Brilliant response to when your site gets hacked
[youtube http://www.youtube.com/watch?v=ILhiW76B3H8&w=560&h=315]
-
2012-01-29
Why is AT&T talking to me in Hebrew bullets?
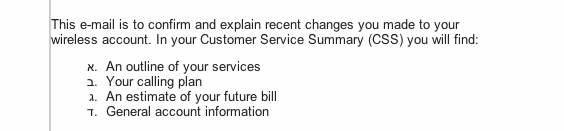
I just received this notification from AT&T. Pretty innocuous, but, what’s up with using Hebrew letters as bullets? Odd.
-
2012-01-24
Keeping emails and security under control
Do you receive tons of notification emails form your various subscriptions or social sites like Twitter and Facebook and the others? Have you thought about the impact on your productivity all these teasers are?
Well, you might have forgotten (or are you too busy to figure out) how to manage or shutdown the notifications. Check out this handy toy that I just came across: Notification Control.
And in a related story, here’s a similar site if you want to review your security and permissions settings on all these sites. Another chore often put off to our own detriment! My Permissions.
Yeah there’s really very little to these two sites but I think you might find them very useful!
-
2012-01-01
TSA: Smokescreening
An interesting and fun to read article in Vanity Fair about the security check procedures established by the TSA:
“Taking off your shoes is next to useless. “It’s like saying, Last time the terrorists wore red shirts, so now weâre going to ban red shirts,” Schneier says. “If the T.S.A. focuses on shoes, terrorists will put their explosives elsewhere. Focusing on specific threats like shoe bombs or snow-globe bombs simply induces the bad guys to do something else. You end up spending a lot on the screening and you haven’t reduced the total threat.” (from: Vanity Fair)
Schneier of course is Bruce Schneier who is always interesting to read. He writes about security and computers. I have quoted him many times before on this blog.
-
2011-11-23
-
2011-11-11
When no response means “no”
Read more →Here’s a tiny social conundrum. When someone writes you, calls you and leave a message, calls and doesn’t, or even texts you, what is your obligation to respond? If the question is “are you free for lunch today” and you know you are not, is it OK to just not answer? If the question is “have you seen this?.”
This seems to come up, and different people and different communities seem to have different rules about this. So before you take offense at the lack of response, consider that it might just be a different social protocol that you may not necessarily adhere to!
I’ve had that happen, though, when leaving several emails or support tickets with services that I use. What do you make of a la...
-
2011-09-28
Swipely, cool but scary?
Read more →So there’s this rather cool new service that says they will find and give you special deals to the stores and merchants you use already. The way they do it is to examine your credit card bills and help you find deals. They say:
With Swipely, you can earn automatic cash back rewards at the best local places Boston has to offer. There are no coupons to cut, vouchers to buy or loyalty cards to forget – with Swipely you earn valuable rewards on every purchase with the credit or debit cards you already have, automatically. Best of all, Swipely is free!
Sounds great, but you know how they do it? You have to give them your credit card info and login to the credit card company web site, so they ca...
-
2011-09-27
New Jersey election fraud? Or coverup? Or just human error?
Read more →Andrew Appelis one of the best known academics studying and commenting on elections and computer science and technology related to elections. He wrote a really interesting report, “New Jersey Elections Coverup“, going into great detail about a specific incident during the June 2011 New Jersey primary election where the reported outcome of a particular race was demonstrated to be incorrect.
It was a small election and so they could literally get affidavits from voters to prove this. Mr. Apple was hired as an expert (apparently he does a lot of this, which for me colors his words to...
-
2011-07-17
BillGuard
This site looks really good, but I am not signing up yet.
I am famously promiscuous signing up with new services just so I can ‘know what’s going on’, but when the first thing I have to do is to give this site my account and password for a credit card that I use, I stop and take a breath.
Who are these guys? Fred Wilson, a highly reputable VC blogger is the one who recommended it in his blog. Maybe he’s an investor? I don’t know. But for now, I am holding off.
-
2011-05-21
[GEEKY] Devise Gem – current favorite for authentication of Rails Applications
How to build authentication into Rails applications? Well, at least at RailsConf 2011, the buzz was around a new Authentication gem called Devise.
I played with it a little (here in the airport) at it seems quite nice and straightforward. Check it out if you were looking for something like that.
railsconf
-
2010-12-14
Wikileaks
Read more →Like many, I don’t know yet whether I support or condemn the Wikileaks action that has been discussed and debated at length on all fora. You have to agree that it has yielded some interesting insights about the way the world works.
First of all: as far as a diplomat making snide comments about one world leader or another, big deal! I mean it’s embarrassing (like someone hacking your email account or finding your personal diary) but certainly no one is surprised — gossiping and show boating is human nature, yes?
A friend of mine who has been in the foreign service for a long time read the cables with gusto and said if nothing else, it shows that the US foreign servic...
-
2010-12-01
Amazing Stuxnet story
Read more →With apologies for quoting a Foxnews story, and with thanks to Scott Adams for the link, here’s a fascinating behind the scenes story of Stuxnet: “The mission: Infiltrate the highly advanced, securely guarded enemy headquarters where scientists in the clutches of an evil master are secretly building a weapon that can destroy the world. Then render that weapon harmless and escape undetected.” (from Mystery Surrounds Cyber Missile That Crippled Iran’s Nuclear Weapons Ambitions)
and how well did it work?
““We brought it into our lab to study it ...
-
2010-11-24
Facebook security
Read more →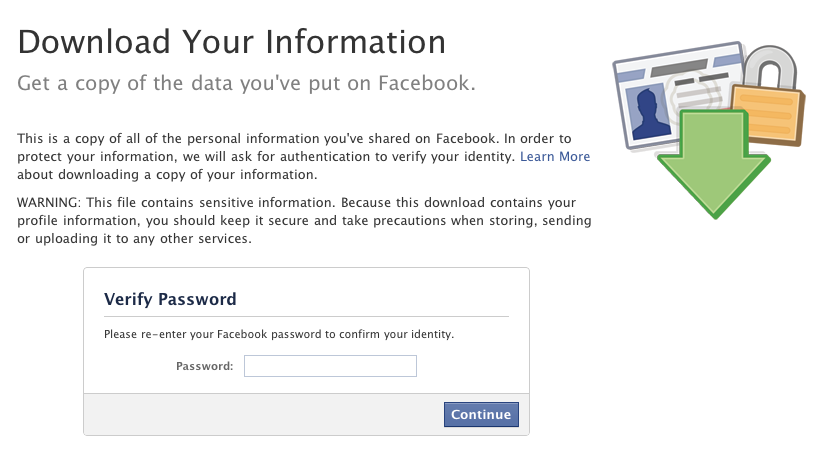 I was experimenting with a little known feature in Facebook, “Download Your Information” which will actually supposedly give you a copy of everything that is ‘yours’ on Facebook. The definition of what is ‘yours’ is fairly tricky of course: is what you posted on someone else’s wall ‘yours’ or ‘theirs’? And so on.
But what interested me was how they made double and triple sure that in fact it was me who was downloading my information.
I had to supply my own password again: ok that makes sense.
But then for ext...
-
2010-09-09
The Tor Anonymizer
Have you heard of this thing, the Tor Anonymizer? Ok again admittedly another highly geeky system, but pretty fascinating. Makes you think that the handwringing worrying of the security wonks isn’t as over the top as all that. Tor is a sophisticated privacy tool designed to prevent tracking of where a web user surfs on the internet and with whom a user communicates. It’s endorsed by the Electronic Frontier Foundation and other civil liberties groups as a method for whistleblowers and human-rights workers to communicate with journalists, among other uses. (from Rogue Nodes Turn Tor Anonymizer Into Eavesdropper’s Paradise
Read the article, it’s a fascinating look into the world of security.
-
2010-09-06
Location Proofs
Read more →The more businesses reward me for showing up at their establishments, the more likely it will be that a bad guy would want to pretend that they were there to garner those rewards. I came across a very interesting paper that proposes the notion of ‘location proofs.’: Enabling new mobile applications with location proofs)
From the paper: “Location is rapidly becoming the next “killer application” as location-enabled mobile handheld devices proliferate. One class of applications that has yet-to-emerge are those in which users have an incentive to lie about their location. These applications cannot rely solel...
-
2010-05-05
Spy vs. Spy
Read more →Here’s a great article by Malcolm Gladwell in The New Yorker about espionage. Most of the content comes from a couple of books that he essentially is summarizing, but in his inimical style make more fun and fascinating: He tells the U.S. Ambassador that the Soviets have broken the Americans’ secret code. “We know they know our code,” the Ambassador, Moulsworth, replies, beaming. “We only give them things we want them to know.” The general pauses, during which, the play’s stage directions say, “he tries to make head or tail of this intelligence.” Then he crosses the street to the Russian Embassy, where he ...
-
2010-04-26
CAPTCHA’s cracked
Read more →CAPTCHA is the nickname of the venerable (ok only a few years of veneration) technique of verifying if the person on the other side of the screen is actually a person not a computer. We’ve all seen them a million times: a very hard to read bit of text in a small box, with a request that you decipher it and type in the text into another box. Well it seems that spammers have figured out a way to defeat them: yes, you guessed it, “Captcha Farms.” I first thought they were some exaggerated fear mongering but I suppose their commonplace enough that it’s being reported even in, the, g-u-l-p, New York Times:
...
-
2010-04-23
Security by obscurity and other slogans
Read more →If you’ve been in computing for any time you may have been hit over the head by the slogan “Security by Obscurity is No Security”. As I have understood the argument it has a few components:
If your security relies on secret tricks, trap doors, and a hope that no one will be able to find out or guess the work around, then you’re fooling yourself. Sooner or later someone will be able to guess the trick, see the code, quit your company and take the secret with them. Allowing your code and methods to be inspected and analyzed by the public (bad guys included) is the only way to learn about weaknesses that you would be blind to and give you a chance to close them. The other slogan which I will t...
-
2010-01-15
Stop treating Americans like idiots and cowards
Read more →An excellent article in the Wall Street Journal about the way the media and politicians want us to react to the recent Christmas Day attempted terrorist attack. “No amount of statistical evidence, however, will make any difference to those who give themselves over to almost completely irrational fears. Such people, and there are apparently a lot of them in America right now, are in fact real victims of terrorism. They also make possible the current ascendancy of the politics of cowardice—the cynical exploitation of fear for political gain.” (from ...
-
2009-12-14
Facebook and Twitter Hacking
Read more →I guess it’s not surprising that people’s Facebook and twitter accounts are getting compromised. From the New York Times: ...
-
2009-04-08
Great paper about Harri Hursti’s demonstration of ballot scanner security concerns
Read more →I recently saw the movie Hacking Democracy. It’s absolutely fascinating and basic background for anyone interested in election reform. In it you learn about some of the heroes of election reform, including Harri Hursti who demonstrates in a pretty dramatic manner some of the weaknesses of commonly used election technology. This is from the wikipedia article:
“Seven participants made out their ballots using the opti-scan paper sheets (Hursti remaining outside the test area). Sancho then went to Hursti and gave him a ballot which Hursti filled out. Hursti then gave Sancho the memory card to insert in to the machi...
-
2008-01-03
Phone spam, charities and trust
In the New York Times, an editorial talks about a study that reveals rampant abuses in certain charitable causes(or organizations passing themselves as such) “The public has rightly shown its empathy with wounded and troubled war veterans, contributing hundreds of millions of dollars to private charities that claim to have the veterans’ best interests at heart. A new study details rampant abuses of the money flow.” (from New York Times)
The study referenced is from a very reputable outfit, Charity Watch.
I haven’t done a careful comparison, as the names of charities that call my house have many very similar sounding names. But my experience in dealing with them on the phone has been almost uniformly unpleasant: strange hard-sell tactics, rudeness, accusations and so on. I had my suspicions and this new study kind of corroborates them.